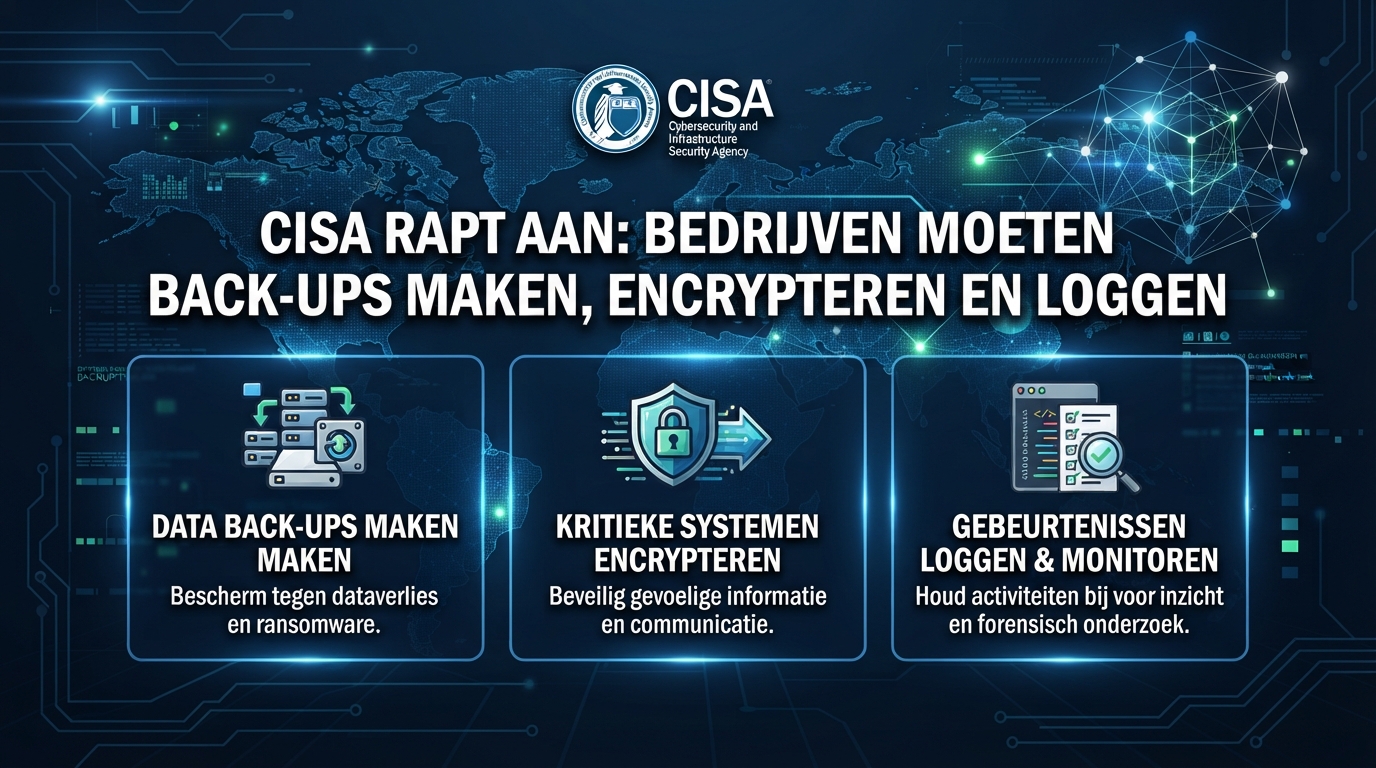
CISA recommends logging on business systems, backing up business data, encrypting business data, and sharing incident information with CISA. The guidance focuses on practical defenses that help organizations detect, recover from, and report cyber incidents.[4]
https://www.cisa.gov/resources-tools/resources/level-your-defenses-four-cybersecurity-best-practices-businesses