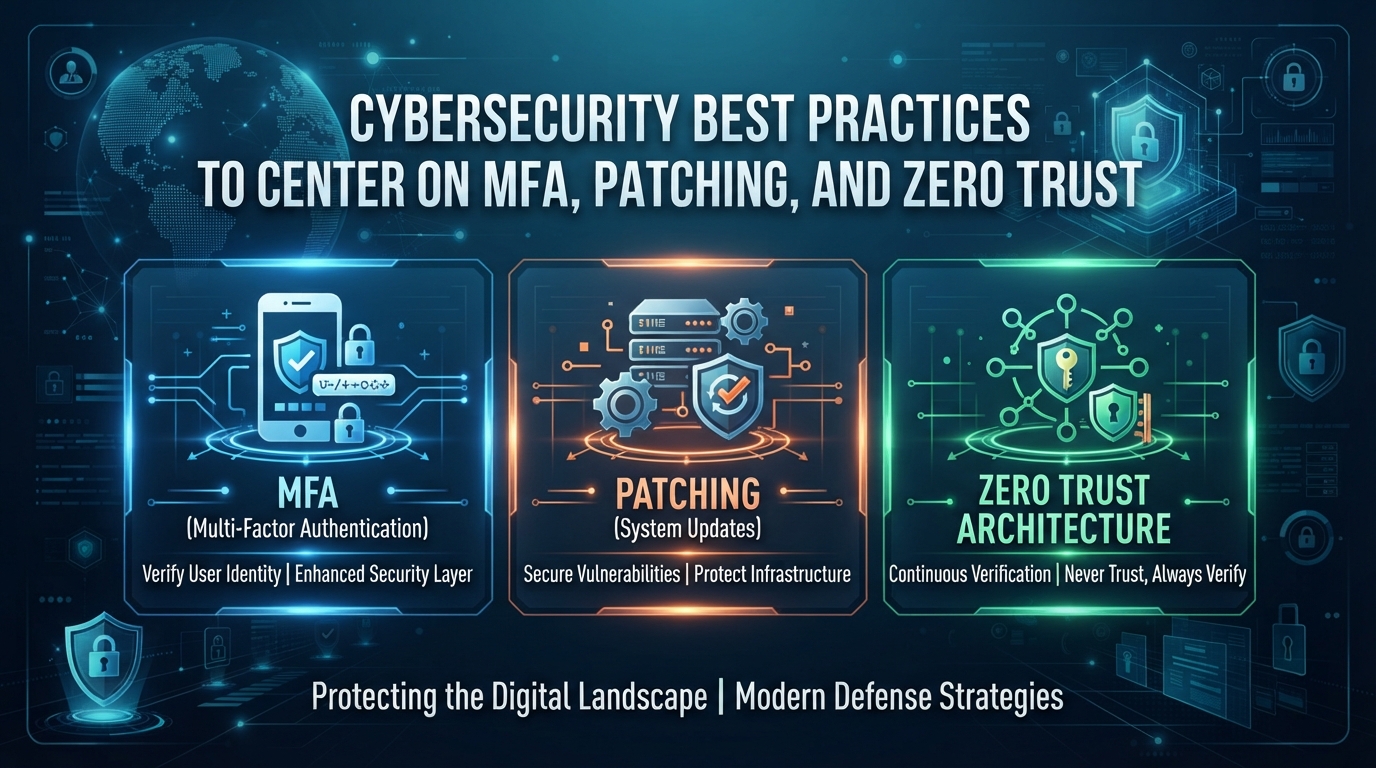
Current guidance emphasizes zero trust, multi-factor authentication, identity and access management, endpoint detection and response, and regular patching. These controls are presented as core defenses against credential theft, endpoint compromise, and lateral movement.[5]
https://www.fortinet.com/resources/cyberglossary/cybersecurity-best-practices